CardEye
International card payment gateway for iGaming merchants, built from scratch
- Role
- Fintech Solutions Architect and Technical Lead, Developers Studio
- Period
- 2021 – 2026
- Status
- Retired in 2026
- transactions a day
- 7,000+
- active merchants
- 10
- BIN records, live
- 1M+
- engineers led
- 7–8
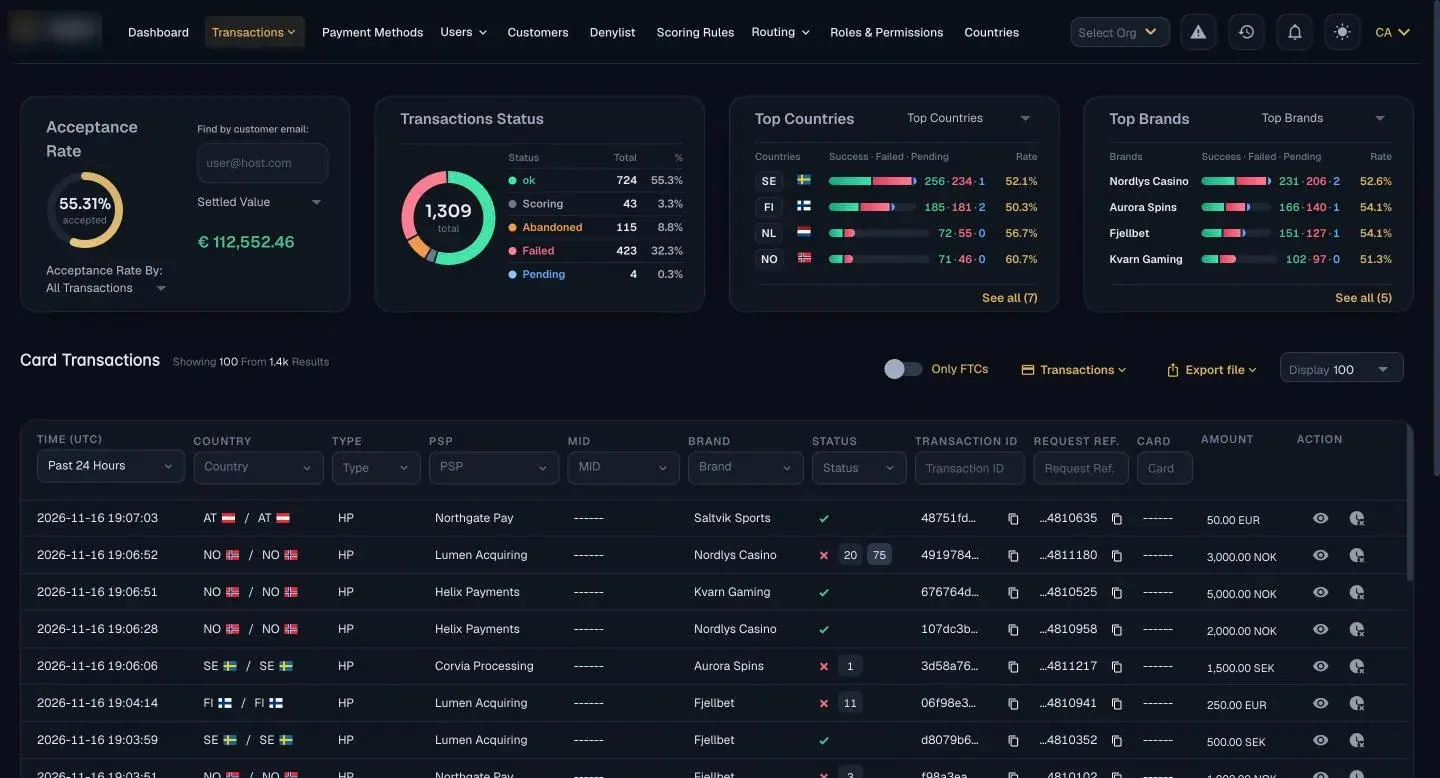
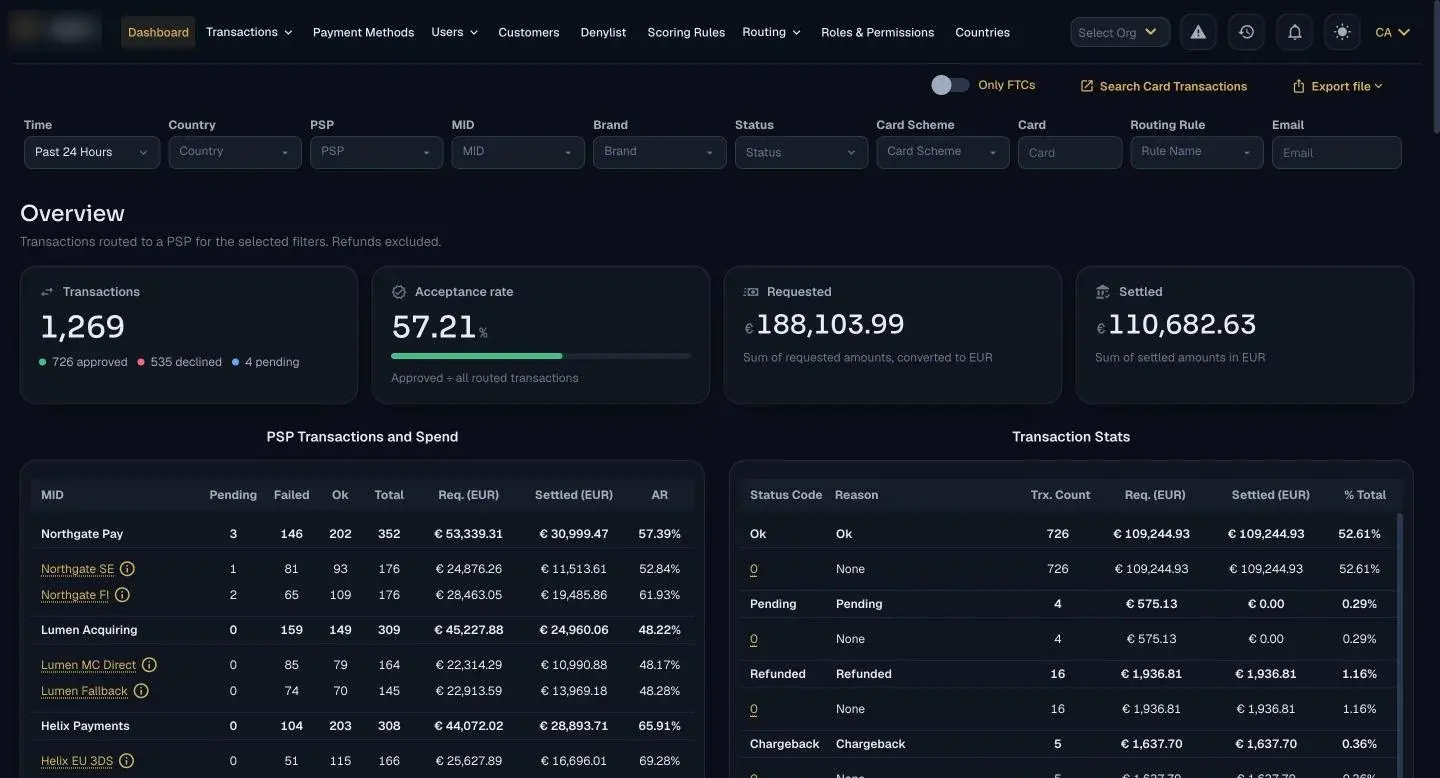
Overview
A PCI DSS card payment gateway designed and built from an empty repository, scaled to 7,000+ transactions a day across 10 active merchants.
CardEye is an international card payment gateway whose merchants were iGaming operators. I owned it end to end: architecture, operations, merchant integrations and compliance.
The challenge
A payment gateway cannot pause while it grows. The database, the BIN data, the provider integrations and the compliance programme all had to change while transactions kept flowing.
Approach
- 01
Changing the database under live load
Migrated the production database from SingleStore to MariaDB while the system was handling live transactions, with no downtime and no data loss. The most operationally complex work I have done.
- 02
Keeping the hot path untouched
Built a BIN ingestion pipeline that loads more than a million records by decoupling the write path from the lookup every live transaction depends on. Bulk merchant exports of 1M+ records run on queues for the same reason.
- 03
One language for failure
Normalised error codes from multiple PSPs into a single unified layer, rolled out with no downtime, so declines are comparable across providers and root-cause analysis is faster.
- 04
Security as architecture
One-time token authentication for the hosted payment page, encryption, application-level rate limiting and SEON fraud screening.
- 05
PCI DSS, every quarter
Owned compliance as the focal point for the QSA, Risk Associates: quarterly reviews, ASV scans, and remediation of findings through to closure.
- 06
A team with standards
Led 7 to 8 engineers through architecture reviews, sprint planning and releases, and set the code review, API and branching standards.
What the clients said
“It has been a privilege to work the past 1.5 years with Wasim on a payment processing database which he has been Project Manager and Team Lead for and has built with his team. What I have enjoyed the most is the thorough documentation he has provided. Flawless.”
 Katie HagströmDirectorClient on CardEye · 1.5 years
“I've worked with Wasim for 1.5 years now for a payment gateway project of which Wasim is the technical manager, and I wholeheartedly recommend him for any similar role. Wasim not only has a deep understanding in the technology side like database and software, but also is an exceptional communicator.”
 Li JiProduct owner, LeoCardClient on CardEye · 1.5 years
Outcome
- Scaled from zero to 7,000+ daily transactions across 10 active merchants
- Full PCI DSS compliance maintained on a live gateway
- PSP and bank integrations, on-ramp and off-ramp flows, open banking and KYC provider integrations, refunds and chargebacks delivered on the platform
Technologies
- PHP
- Laravel
- MariaDB
- SingleStore
- React.js
- REST APIs
- Queues
- CI/CD
- SEON
Screens are from the platform running locally on test data. Merchant, provider and customer names shown are not real.
Next project
Multi-PSP channel operations
Open to consulting engagements
Have a payment problem that needs tracing?
Tell me which providers are involved and what is going wrong, or what needs to go live. I will tell you plainly whether I can help.
- Tell me
- Which providers and markets are involved
- Show me
- What is failing, or what needs to go live
- You get
- A plain answer on whether I can help